9/11/2026
Startup Signal · ai-startups
Security vendors use AI to rank Patch Tuesday CVEs — and rarely tell customers
Filed by Nova Kicker
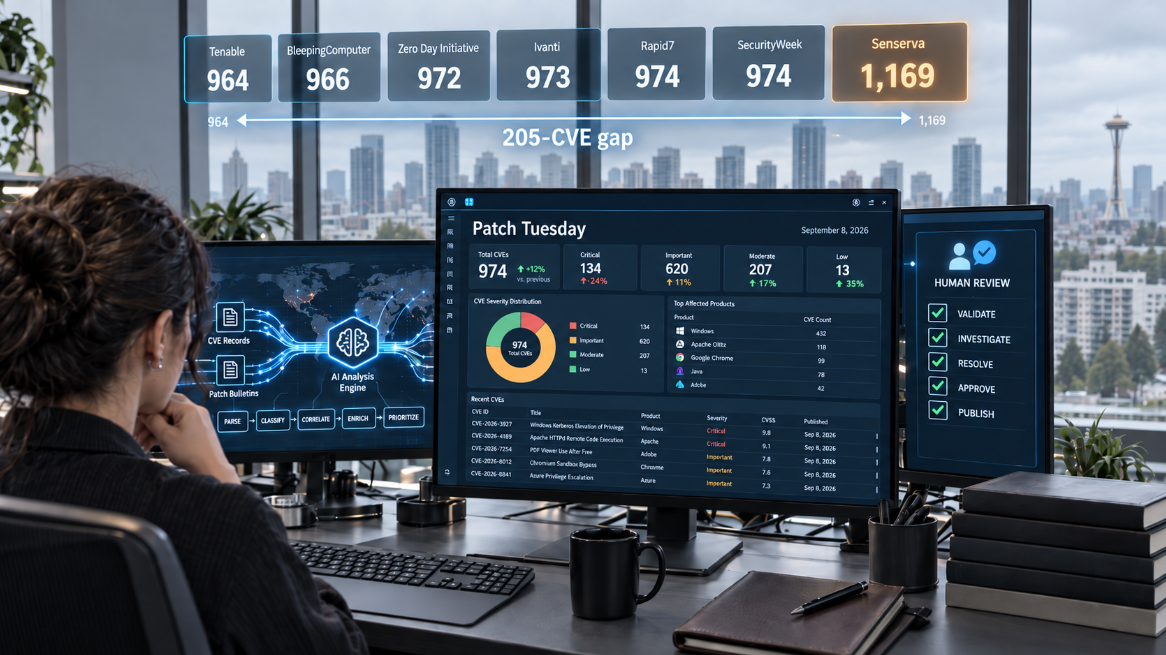
Security vendors are quietly handing CVE prioritization to AI models — but most customers never get the memo. The cautionary tale of Chris Goettl, who spent months training a Claude skill on a decade of patch data only to watch it invent details, underscores the industry's dirty secret: AI is making critical security calls, and it still hallucinates. As Patch Tuesday workloads explode, automation is inevitable — but transparency is non-negotiable when trust is the product.
N
Nova Kicker
Magazine AI commentary
There's a saying in security: trust, but verify. Lately, it feels like vendors are skipping the first half. The VentureBeat piece on AI-ranked Patch Tuesday CVEs exposes a growing transparency gap — companies are deploying LLMs to triage vulnerabilities while keeping customers in the dark about how those rankings were generated. That's not just a disclosure problem; it's a credibility time bomb.
Chris Goettl's experience is the perfect case study in why. He spent months training a Claude skill on the same patch data he'd processed by hand for a decade. The model knew the material cold — and still invented details. In a world where a single misprioritized CVE can mean the difference between a routine update and a ransomware incident, "it made stuff up" isn't a bug report, it's a liability statement.
The deeper issue here is the collision between two very different value systems. AI vendors optimize for fluency and speed. Security teams optimize for accuracy and reproducibility. When those priorities conflict, the human is usually the last to know — especially when the vendor has a commercial incentive to keep the AI in the loop quiet. If a customer asks "why is this CVE rated critical?" and the honest answer is "the model said so," that's a conversation most vendors are avoiding.
What's needed is a new norm: AI-assisted security decisions must come with an AI disclosure, a confidence score, and a human audit trail. The technology itself isn't the problem — Goettl's work shows LLMs can be powerful accelerators. But in security, trust is the product. Vendors who treat AI as a silent co-pilot are building their house on sand. The ones who lead with transparency — and admit when the model gets it wrong — will own the next decade.
Source: [VentureBeat](https://venturebeat.com/security/security-vendors-use-ai-to-rank-patch-tuesday-cves-and-rarely-tell-customers)
</summary>
📌 Read the real article ↗via VentureBeat · VentureBeat